Facebook
Business account disabled
Sign in from your laptop instead of your desktop and the account asks to verify you again -- because the same environment does not present the same fonts, voices and hardware on both. GekkoLogin syncs the whole environment encrypted, so the second machine opens as the first one, and only one machine may hold it at a time.
The problem
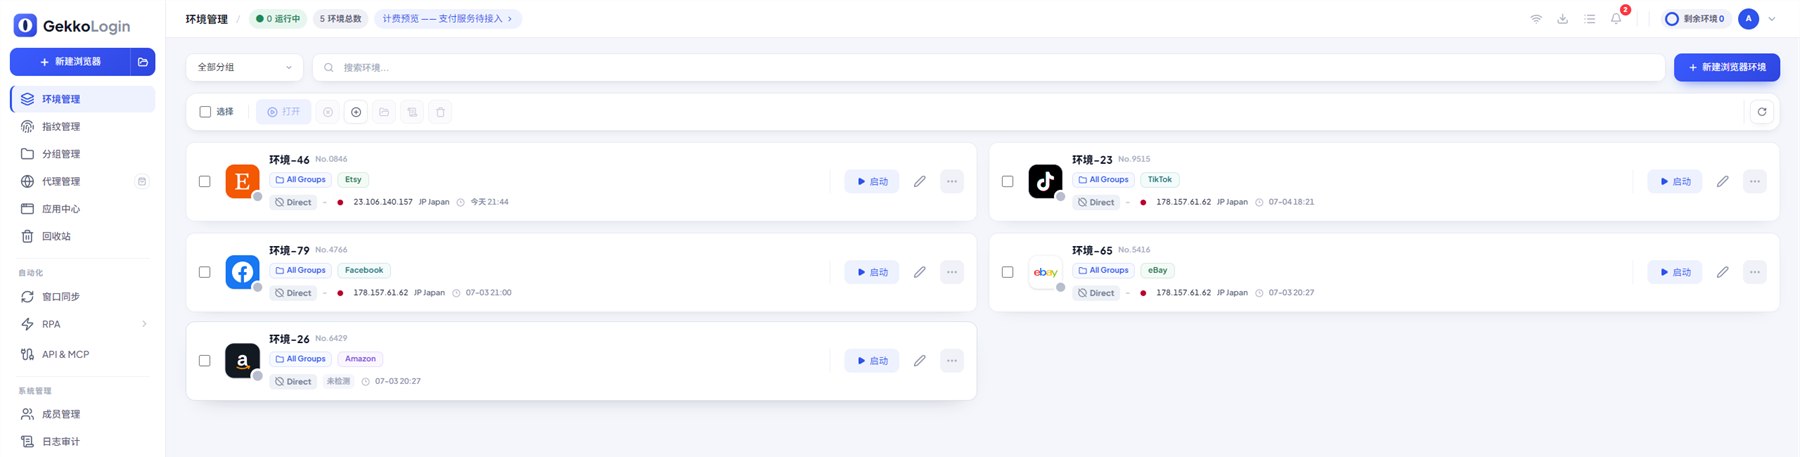
One shared browser leaks repeated cookies, IP context and device signals. GekkoLogin creates a separate, stable environment for every account to keep sessions private and independent.
Business account disabled
Campaign suspended
Shop restricted
Seller review
Listing limits
Why it works
Platforms do not only look at an account password. They compare browser state, device signals, IP context and repeated behavior. GekkoLogin packages those signals into isolated, stable profiles so each account works from its own coherent environment.
Explore browser fingerprintingCanvas, WebGL, fonts, language, timezone and device fields need to tell one consistent story.
Cookies, local storage, cache and session history stay inside the profile assigned to that account.
Proxy location, timezone, language and geolocation context should match the market you operate in.
Use cases
Keep each campaign or client workspace fully isolated, with its own private browser identity and network context.
Manage multiple stores on Amazon, Shopify, Shopee, Temu and eBay with separate regional context.
Operate wallets, quests and airdrop workflows while keeping browser, proxy and session state isolated.
Run repeatable browser data workflows with controlled fingerprints, cookies and network settings.
Separate client workspaces, campaign accounts and operator access without mixing credentials or storage.
Scale campaigns across Facebook, Instagram, Telegram, TikTok and more while keeping accounts apart.
Product controls
A coherent fingerprint that holds the same on every launch — canvas, WebGL, fonts, timezone and hardware move together, so a profile never drifts or contradicts itself.
Learn moreRun every account from its own cookies, storage, proxy, fingerprint and history.
Learn moreCreate, group, edit, import and export profile sets without repetitive setup work.
Learn moreAssign HTTP or SOCKS5 proxies and keep location context consistent with profiles.
Learn moreRepeat controlled actions across multiple profile windows when operators need scale.
Learn moreTurn repeat browser steps into reusable workflows while keeping manual control nearby.
Learn moreStart profiles from local tools and connect automation through browser debugging endpoints.
Learn moreControl profile ownership, member access, handoff rules and team activity records.
Learn moreActivation path
Desktop products convert only after users see a profile launch cleanly. This path makes the first environment feel concrete instead of abstract.
Install GekkoLogin and sign in to the workspace that owns your profiles.
Choose the account type, assign a proxy and keep storage isolated from other accounts.
Confirm IP, timezone, language, WebRTC and fingerprint context before opening the account.
Open the profile, run repeat tasks, export when needed or share access with a teammate.
Product evidence
See how profile state, browser signals, updates and team access are controlled before you move important accounts into a new workspace.
Profiles keep cookies, cache, extension state and local storage inside dedicated profile directories.
Each launch can verify proxy, country, timezone, WebRTC and browser context before account work begins.
Browser core, fonts, extensions and app updates can be explained through changelogs instead of hidden changes.
Teams can separate account ownership, operator permissions, profile groups and activity review.
Automation
Developers and operators should be able to start profiles locally, connect Playwright, Puppeteer or Selenium, and later route agent workflows through MCP without changing the browser profile model.
POST http://localhost:35000/api/v1/profile/start
{ "profileId": "8f2a-c41d-..." }

// returns a CDP endpoint
{ "port": 51944, "ws": "ws://127.0.0.1:51944/..." }

const browser = await puppeteer.connect({
  browserWSEndpoint: res.ws
})
const page = await browser.newPage()
Team control
The risk in multi-account work is rarely the platform. It is a profile copied onto a laptop, a password passed around, a machine nobody remembers granting. Each of those is a mechanism here rather than a policy, and you can check every one of them.
Read about securityEnvironment data is encrypted before it leaves your machine and every device holds its own key. The server never sees plaintext.
The first time a device reads an environment, it asks you -- comparing a fingerprint with the person at that machine.
An open environment is held by exactly one device. The second is refused rather than allowed to diverge from the first.
Who opened which environment, when, from which device and which address.
Resources
FAQ
Start with a real desktop environment, run the launch check, then open the account from a cleaner context.